Architect, migrate, and operate mission-critical workloads across AWS and Google Cloud Platform. From zero-downtime database cutovers to automated Kubernetes orchestration and FinOps cost optimization.

Delivering enterprise resilience, hardened security postures, and sub-second global transaction speeds across hybrid and multi-cloud environments.
Seamless lift-and-shift, re-platforming, and cloud-native refactoring for legacy enterprise systems. We handle multi-terabyte database transfers with zero downtime.
Production-grade EKS, GKE, and self-managed Kubernetes clusters configured for high availability, zero-downtime rolling updates, and dynamic horizontal pod autoscaling.
100% reproducible, auditable cloud environments managed via Terraform, Terragrunt, and AWS CDK. Automated security linting and policy enforcement before any deployment.
Eliminate wasted spend with automated rightsizing, spot instance orchestration, savings plans, committed use discounts, and granular departmental cost-allocation tags.
Enterprise zero-trust architecture. Identity federation, least-privilege IAM policies, KMS envelope encryption, and automated compliance auditing for ISO 27001, HIPAA, and PCI-DSS.
Event-driven backends using AWS Lambda, Google Cloud Run, EventBridge, and Pub/Sub. Infinite auto-scalability from zero to millions of invocations with zero idle infrastructure costs.
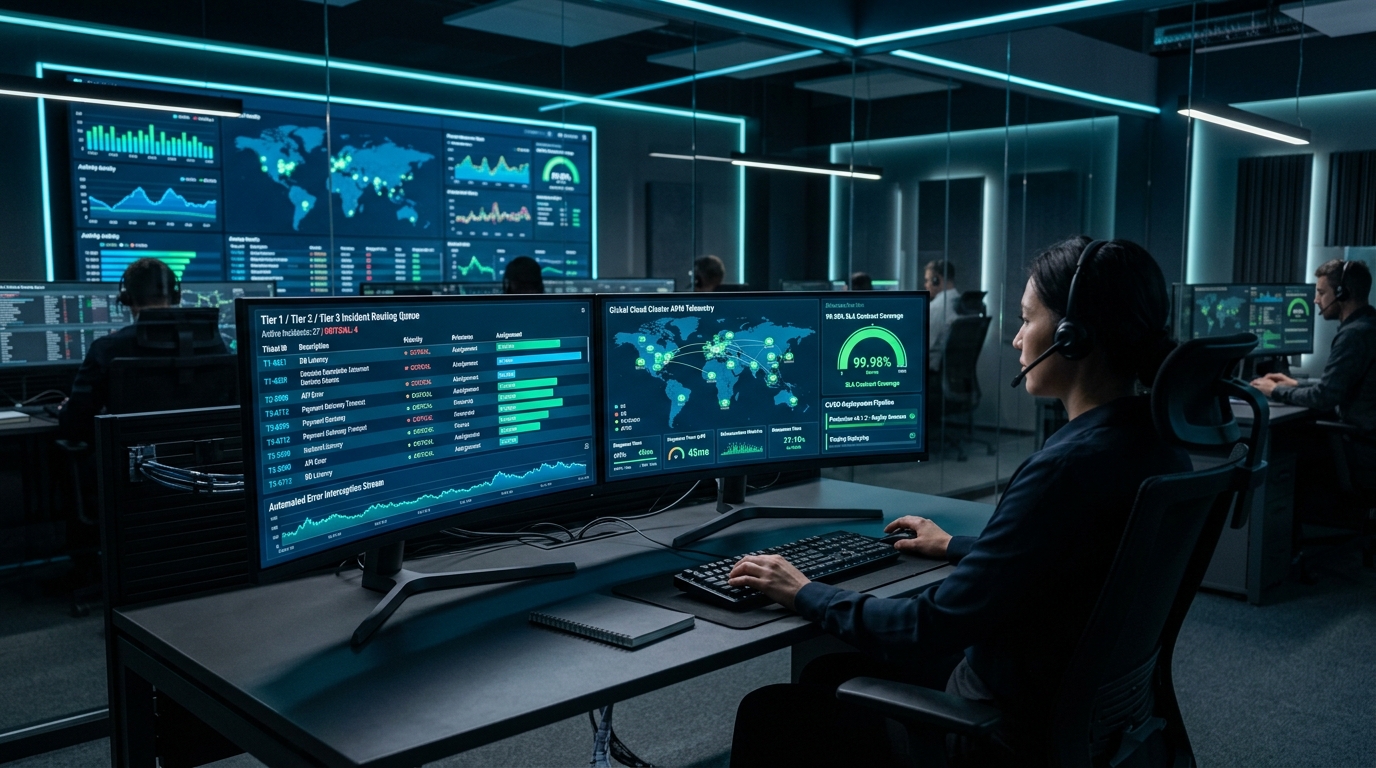
iCanSoft engineers build fault-tolerant topologies spanning multiple Availability Zones and regions, ensuring seamless automatic failover even during major cloud provider outages.
Distributed Application Load Balancers (ALB) and Cloud Load Balancing with health-checked automatic traffic diversion.
Sub-minute RTO and RPO for transactional MySQL, PostgreSQL, and document stores with global read replicas.
Ultra-low latency dedicated 10Gbps fiber interconnects bridging on-premise data centers with AWS Direct Connect and Google Cloud Interconnect.
From infrastructure audit and architectural blueprinting to zero-downtime cutover and 24/7 SRE management.
Audit current architecture, identify workload dependencies, and deliver concrete TCO reduction estimates.
Provision secure multi-account organizational structures, IAM guardrails, and VPC topologies via Terraform.
Execute continuous background data replication, dry-run cutover rehearsals, and perform zero-downtime DNS switches.
Continuous telemetry monitoring, proactive vulnerability patching, and monthly cost optimization reviews.
Schedule an architectural deep dive with our AWS and Google Cloud certified architects to review your scalability, uptime, or migration roadmap.
Direct response from our certified cloud architect within 24 hours.